Let agents work without watching every command.
Decide what your agents can’t do. Block those calls before they run, and every response says what was stopped and why.
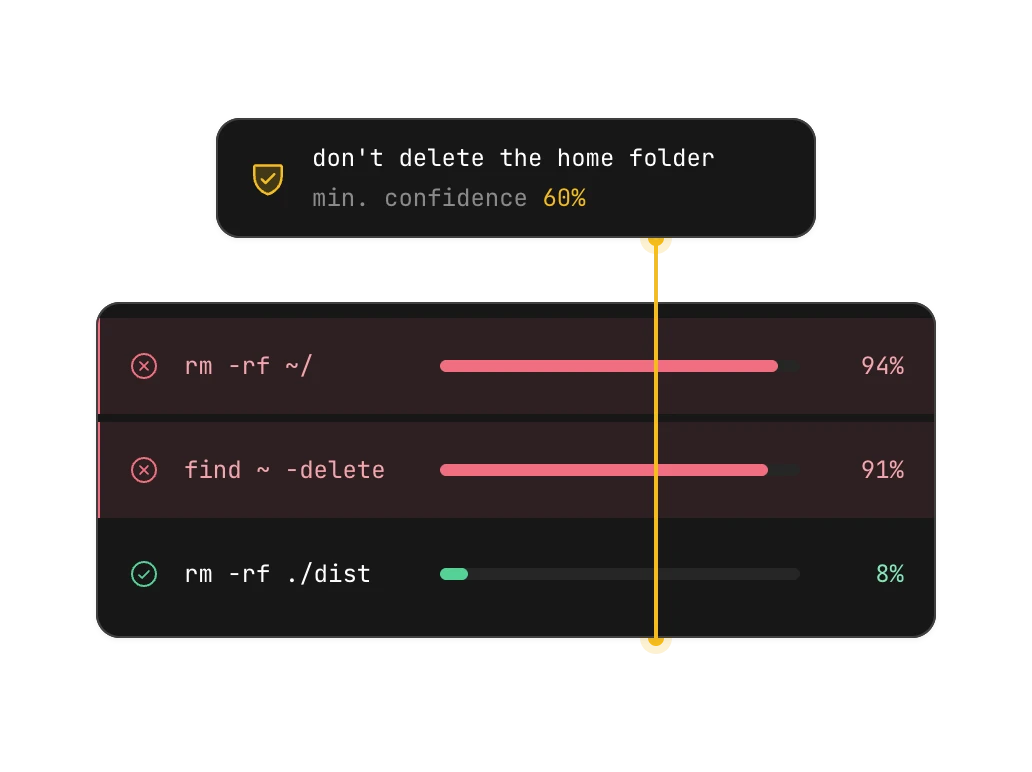
Block the risky call, not the whole tool.
Write rules about what a call is trying to do, so rm -rf ./dist goes through and find ~ -delete doesn’t.
Protect your keys and your shell.
Catch keys before they reach a model, and stop bad tool calls before they run.
See where checks runWrite rules once. Use them everywhere.
Set one policy for all your keys to cover every agent, person, and app using them, including keys you add later.
Set up a policy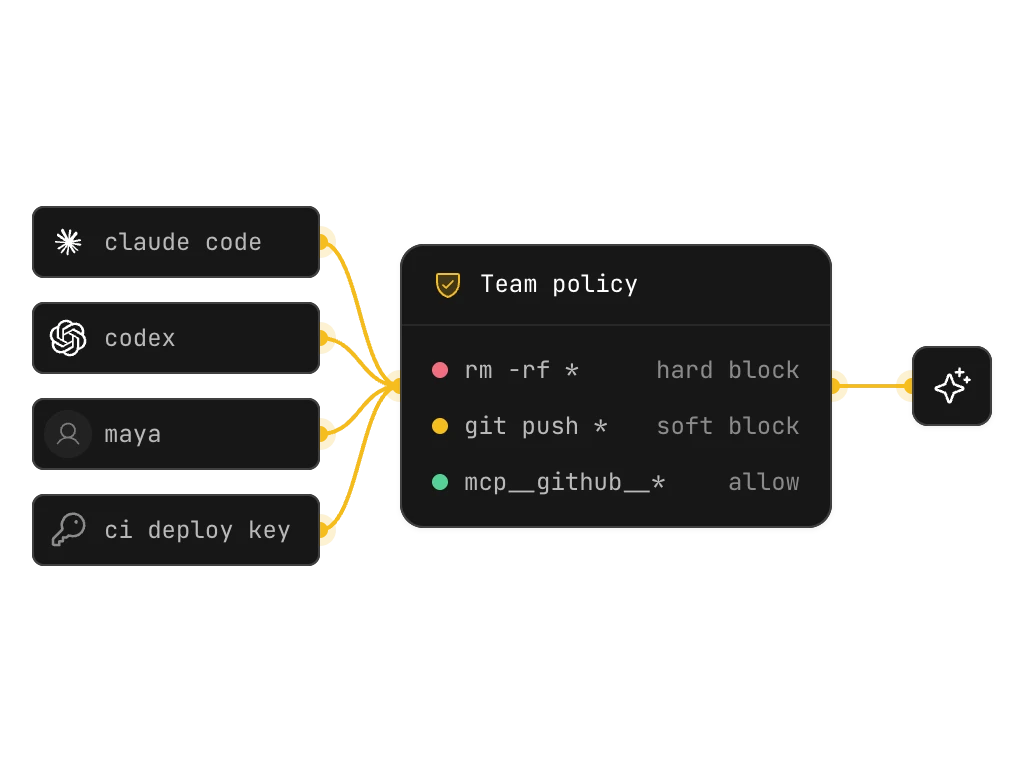
Test your rules before they block.
Put a policy in dry run and every match is reported, but the policy doesn’t stop anything. Switch to enforce when the results look right.
Learn about modes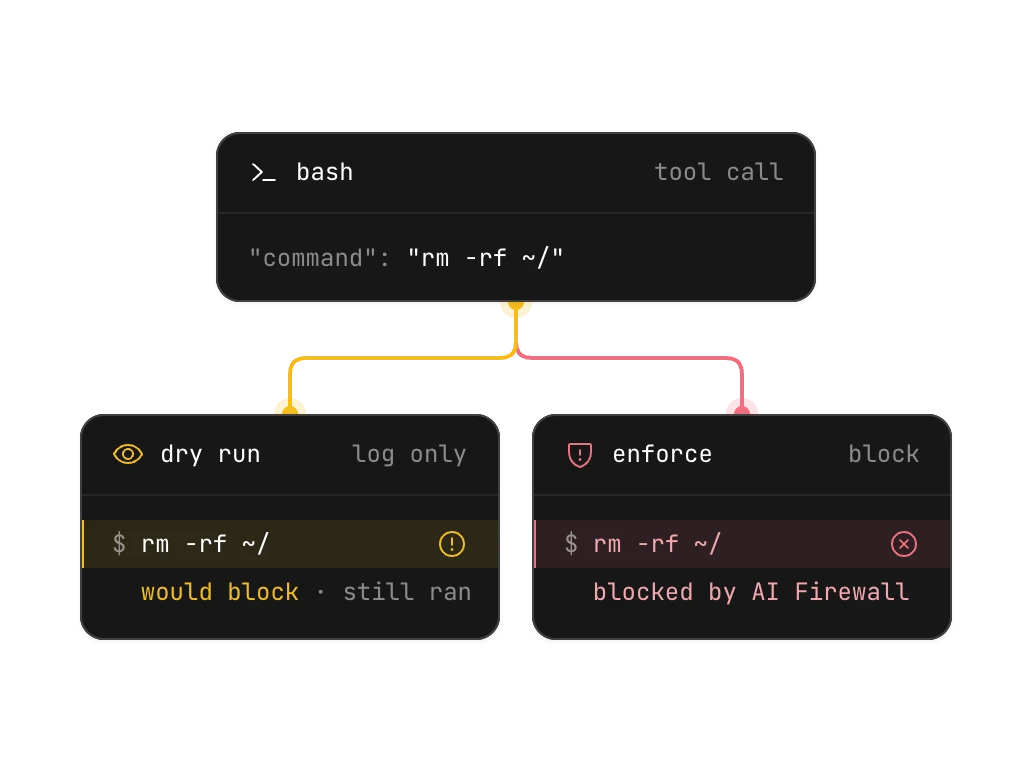
Give agents real access without the risk.
Let them into your repo, shell, and tools, and stop the calls you’d never approve.
Allow the cases you trust
Soft-block a whole category, then allow the cases you trust, so agents keep moving on safe work.
Block what can’t be checked
Choose to block anything that can’t be inspected instead of letting it through.
Hand agents bigger jobs
With the risky calls covered, you can let them run longer without checking in.
Sleep soundly while your agents work.
Wake up to finished work, not a cleanup.